Who is responsible for your data
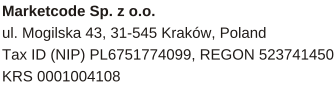
The controller of personal data described in this policy is the operator of outreachauto.com, whose company details are shown in the image below. You can reach us about any privacy matter at [email protected].
What data we collect
We collect only what the site and the service need to work, to stay secure and to bill you correctly.
- Account data: your name, business email address, password hash, workspace name, role and plan.
- Billing data: billing name, billing address, tax number where you provide one, plan, invoices and payment status. Full card numbers are handled by the payment processor and never stored by OutreachAuto.
- Demo inputs: the website address, the offer description and the ideal customer description you enter on the homepage, plus the output generated from them.
- Usage data: pages and features you use, timestamps, IP address, browser type, device type and error logs.
- Support data: the content of messages you send to [email protected].
- Connected inbox data: when you connect your own inboxes, the connection settings and authorisation tokens needed to send and read campaign mail on your behalf.
Cookies
OutreachAuto uses only cookies that are strictly necessary: a session cookie that keeps you logged in, a security token that protects forms against cross site request forgery, and a cookie that remembers your consent choices. We do not use advertising cookies. Because these cookies are necessary for the service, they do not require consent, and they expire when your session ends or shortly after.
Why we use your data and on what legal basis
| Purpose | Data | Legal basis under GDPR |
|---|---|---|
| Creating and running your account and workspaces | Account data, connected inbox data | Performance of a contract, Article 6(1)(b) |
| Running the homepage demo and showing your result | Demo inputs | Performance of a contract at your request, Article 6(1)(b) |
| Billing, invoices and tax records | Billing data | Legal obligation, Article 6(1)(c), and contract |
| Security, fraud and abuse prevention | Usage data | Legitimate interest in protecting the service, Article 6(1)(f) |
| Improving features and fixing errors | Usage data in aggregated form | Legitimate interest, Article 6(1)(f) |
| Transactional emails such as sign-in codes and receipts | Account data | Performance of a contract, Article 6(1)(b) |
| Answering support requests | Support data | Contract or legitimate interest, Article 6(1)(b) and (f) |
Creating and running your account and workspaces
- Data
- Account data, connected inbox data
- Legal basis under GDPR
- Performance of a contract, Article 6(1)(b)
Running the homepage demo and showing your result
- Data
- Demo inputs
- Legal basis under GDPR
- Performance of a contract at your request, Article 6(1)(b)
Billing, invoices and tax records
- Data
- Billing data
- Legal basis under GDPR
- Legal obligation, Article 6(1)(c), and contract
Security, fraud and abuse prevention
- Data
- Usage data
- Legal basis under GDPR
- Legitimate interest in protecting the service, Article 6(1)(f)
Improving features and fixing errors
- Data
- Usage data in aggregated form
- Legal basis under GDPR
- Legitimate interest, Article 6(1)(f)
Transactional emails such as sign-in codes and receipts
- Data
- Account data
- Legal basis under GDPR
- Performance of a contract, Article 6(1)(b)
Answering support requests
- Data
- Support data
- Legal basis under GDPR
- Contract or legitimate interest, Article 6(1)(b) and (f)
We do not sell personal data and we do not use it for automated decisions that produce legal effects for you.
Your data versus your campaign data
For your account, billing and usage data, OutreachAuto acts as controller. For the prospect and contact data you import or build in the service, and for the content of your campaigns, you are the controller and OutreachAuto acts as your processor. That processing follows your instructions and the Data Processing Agreement. You are responsible for having a lawful basis to contact your prospects; see our cold email compliance page for how the product supports this.
Data about prospects
When you build a prospect list, OutreachAuto reads public company websites and public business signals and combines them with the contacts you import. It processes business contact data only, never special categories of data. Every campaign email carries an unsubscribe link and header, and an opt-out goes to one suppression list for the whole account. A prospect who wants their data removed can write to [email protected] and we pass the request to the responsible customer and delete it from the suppression process where the law allows.
Who receives your data
We share personal data only with service providers that help us run OutreachAuto, under written agreements that bind them to confidentiality and security. We name them by category.
- A hosting provider in the European Union that stores the application and its databases.
- An email delivery provider that sends transactional mail such as sign-in codes and receipts.
- A payment processor that handles subscriptions, card payments and invoices.
- An AI model provider that generates offer analysis, account briefs and email drafts from the inputs you give.
- A network and security provider that protects the site against attacks and delivers it quickly.
We also disclose data where the law requires it, for example to a court or a tax authority.
International transfers
Some providers process data outside the European Economic Area. Where that happens, transfers are covered by the standard contractual clauses approved by the European Commission, or by an adequacy decision, together with additional safeguards such as encryption in transit and at rest. You can request a copy of the relevant safeguards at [email protected].
How long we keep data
- Demo runs made without an account are kept for 7 days and then deleted.
- Account and workspace data is kept while your subscription is active and deleted within 30 days after you close your account, unless you export it first.
- Billing records are kept for the period required by tax and accounting law.
- Security logs are kept for up to 12 months.
- Suppression entries are kept as long as needed to honour the opt-out.
Your rights
Under GDPR you have the right to:
- access the personal data we hold about you,
- have inaccurate data rectified,
- have your data erased,
- restrict processing,
- receive your data in a portable format,
- object to processing based on legitimate interest,
- withdraw consent at any time where processing is based on consent.
To use any of these rights, write to [email protected]. We answer within one month. You also have the right to lodge a complaint with a data protection supervisory authority, in particular in the country where you live, work or where the alleged infringement took place.
How we protect data
Data is encrypted in transit and at rest, access is limited by roles, connected inbox tokens are stored encrypted, and administrative access is logged. Read more on the outbound data security page.
Changes to this policy
We update this policy when the service or the law changes. The date at the top shows the latest version. If a change matters to how we use your data, we tell account holders by email before it takes effect.
Contact
Questions about privacy go to [email protected]. You can also read our Terms of Service or use the contact page.