The parties
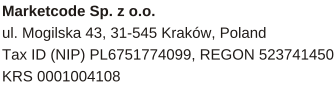
The processor is the operator of outreachauto.com, whose company details are shown in the image below. The controller is the business that holds the OutreachAuto account.
Roles of the parties
You are the controller of the personal data you import into OutreachAuto or create with it for your campaigns. OutreachAuto is your processor for that data. For account, billing and usage data about your own users, OutreachAuto acts as an independent controller as described in the Privacy Policy.
Subject matter and duration
The subject matter is the provision of the OutreachAuto service: building prospect lists, researching accounts, drafting and sending email sequences from your inboxes, preparing LinkedIn tasks, classifying replies, booking meetings and syncing with your CRM. Processing lasts for the term of your subscription and the deletion period that follows it.
Nature and purpose of processing
Processing consists of collection, storage, organisation, enrichment with public business information, analysis, generation of message drafts, transmission of email, classification of replies and deletion. The sole purpose is to deliver the service to you under your documented instructions, which are the terms, this agreement and your settings in the product.
Categories of data subjects
- Prospects and contacts of the customer, including people at companies you target and people who reply to your campaigns.
- Users of the customer's workspaces.
Categories of personal data
- Business contact data: name, job title, company, business email address, business phone number, professional profile address and company location.
- Communication content: emails sent and received through connected inboxes, reply classifications, notes and meeting details.
- Usage data of the customer's users within the service.
No special categories of personal data are processed, and you must not upload them.
Processor obligations
OutreachAuto processes personal data only on your documented instructions, including with regard to international transfers, unless the law requires otherwise; in that case we inform you before processing unless the law forbids it. We tell you promptly if we believe an instruction breaches data protection law.
Confidentiality
Everyone authorised to process the personal data, staff and contractors alike, is bound by a duty of confidentiality and receives access only to the extent needed for their task.
Security measures
OutreachAuto applies technical and organisational measures appropriate to the risk, as required by Article 32 GDPR. In summary:
- encryption of data in transit and at rest, including encrypted storage of inbox authorisation tokens,
- role based access control, single sign-on on Scale and an audit log of administrative actions,
- separation of customer workspaces,
- regular backups and tested restore procedures,
- monitoring, logging and protection against network attacks,
- least privilege access for staff and prompt removal of access when no longer needed.
More detail is on the outbound data security page.
Subprocessors
You give general authorisation for OutreachAuto to engage subprocessors in these categories: a hosting provider in the European Union, an email delivery provider for transactional mail, a payment processor, an AI model provider and a network and security provider. Each subprocessor is bound by written terms that give at least the same protection as this agreement, and OutreachAuto remains responsible for their performance.
Changes and your right to object
We notify account owners by email at least 30 days before adding or replacing a subprocessor. You may object on reasonable data protection grounds within that period by writing to [email protected]. If we cannot address the objection, you may cancel the affected service and receive a prorated refund of prepaid fees for the remaining period.
International transfers
Where personal data is transferred outside the European Economic Area, the transfer is covered by the standard contractual clauses adopted by the European Commission, or by an adequacy decision, together with supplementary measures such as encryption. By accepting this agreement you enter into those clauses where they are needed.
Assistance with data subject requests
The product lets you find, export, correct and delete contact records and add people to the account-wide suppression list. Where you cannot answer a request with these tools, we help you by appropriate measures. If a data subject writes to us directly about your data, we pass the request to you without undue delay and do not answer it ourselves unless you instruct us to.
Further assistance
Taking into account the information available to us, we help you meet your obligations on security, data protection impact assessments and prior consultation with a supervisory authority.
Personal data breach notification
We notify you without undue delay after becoming aware of a personal data breach affecting your data, and give you the information you need to meet your own notification duties: the nature of the breach, the categories and approximate number of people and records affected, likely consequences and the measures taken or proposed.
Deletion or return at the end
When your subscription ends, you can export your data for 30 days. After that period we delete the personal data processed on your behalf, including copies, unless the law requires us to keep it. Backups are overwritten within their normal rotation cycle.
Audits
We make available the information needed to demonstrate compliance with Article 28 GDPR, including a written summary of our security measures on request. Where that information is not enough, you may carry out an audit, by yourself or through an independent auditor bound by confidentiality, with at least 30 days notice, at your own cost, during business hours and no more than once a year, unless a supervisory authority requires otherwise or a breach has occurred.
How this agreement is concluded
On the Scale plan, you can request a countersigned copy of this agreement in the app, in your workspace billing settings. On every other plan, you accept this agreement by creating an account and using the service, and it binds both parties from that moment. If this agreement conflicts with the terms, this agreement prevails for the processing of personal data.
Contact
Questions about this agreement go to [email protected]. Compare what each plan includes on the outbound automation pricing page.